Selasa, 14 April 2020

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

Well, Windows users have a bad habit of removing files from recycle bin. Deleting useless files from Recycle Bin helps a user to save some storage space which can improve the speed of a computer. However, Windows users do that more frequently and later regret. Actually, Recycle Bin is a place from where we can get back our deleted files and folders.
Sometimes, we accidentally delete our important files and folders and due to some reason we lose them from Recycle bin too! At that time, we search for recovery methods. Well, there are many methods available over the web which can help you to recover deleted files from computer, but, when it comes to reliability, nothing can beat EaseUS.

What Is EaseUS Data Recovery Wizard?

EaseUS is one of the leading software providers which is known for its data recovery programme. EaseUS offers some free data recovery software that can help you to recover deleted, formatted or lost data from PC, laptop or removable device easily and quickly.
One of the best thing about EaseUS is that it provides tools for recycle bin recovery which can help you to get back files that you have deleted from the Recycle bin itself. EaseUS Data Recovery Wizard free can easily recover lost files, pictures, documents, videos and more from deleting, formatting, partition loss, OS crash, virus attack and other data loss cases.

How To Recover Deleted Files?

If you are struggling to get back your lost data files, then here is an easy data recovery method which will help you to get back deleted files on your computer. Below, we are going to share a mini guide on how to use EaseUS Recycle Bin Recovery to get back your deleted data.
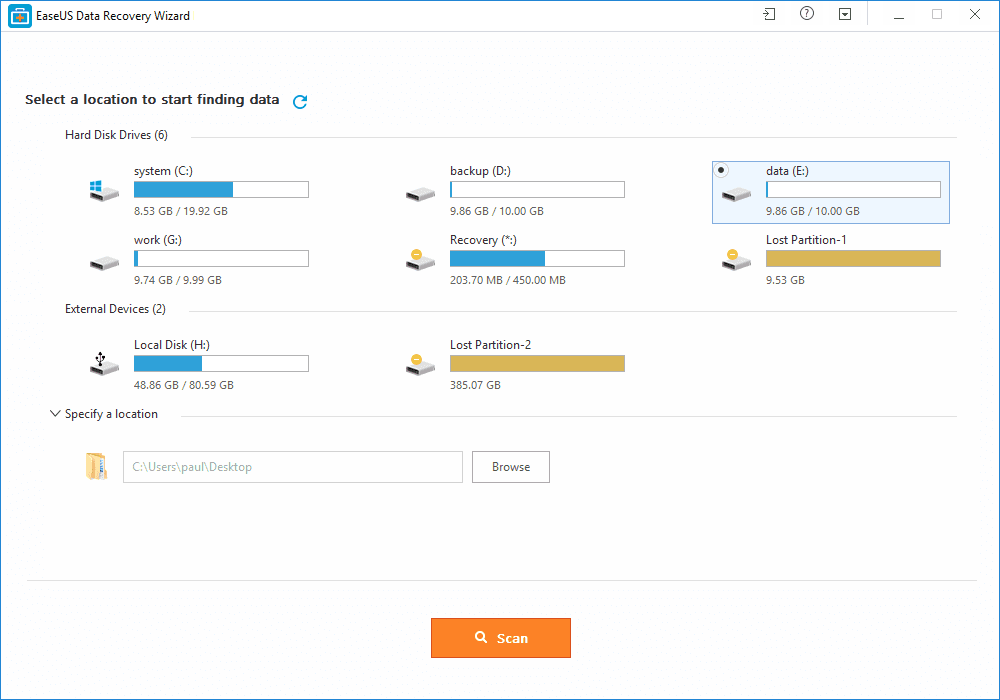
Step 1. First of all, you need to download and install EaseUS Data Recovery Wizard on your Windows computer and then launch it normally. You need to select the location where you want to scan and then click on 'Scan'
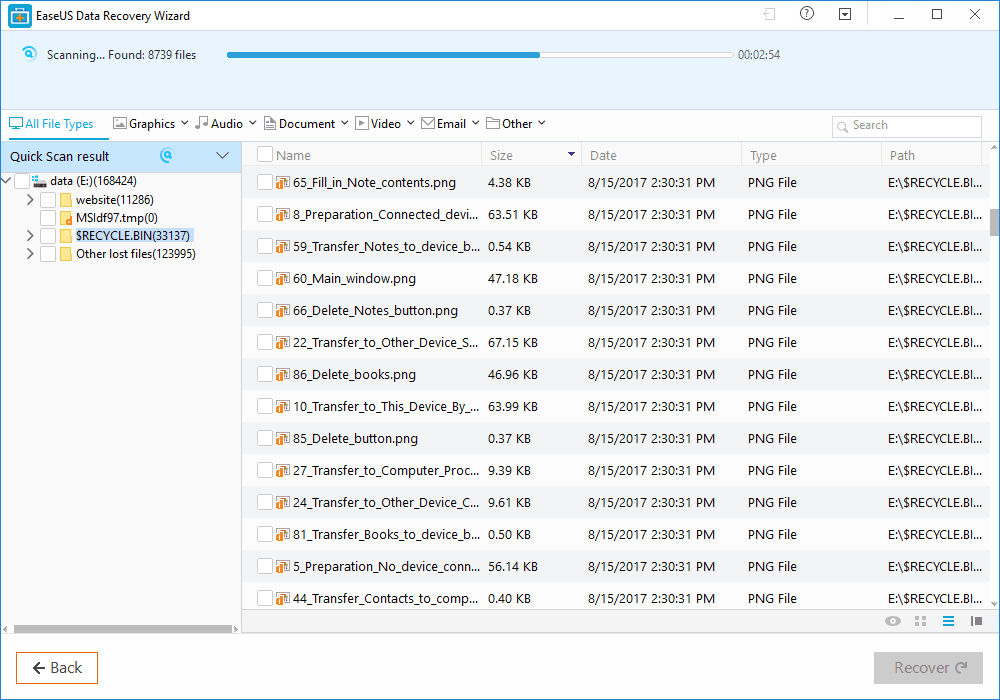
Step 2. Now, wait for few minutes until the tool finishes scanning your drive. The tool search for files that got deleted or cleaned from the Recycle Bin.
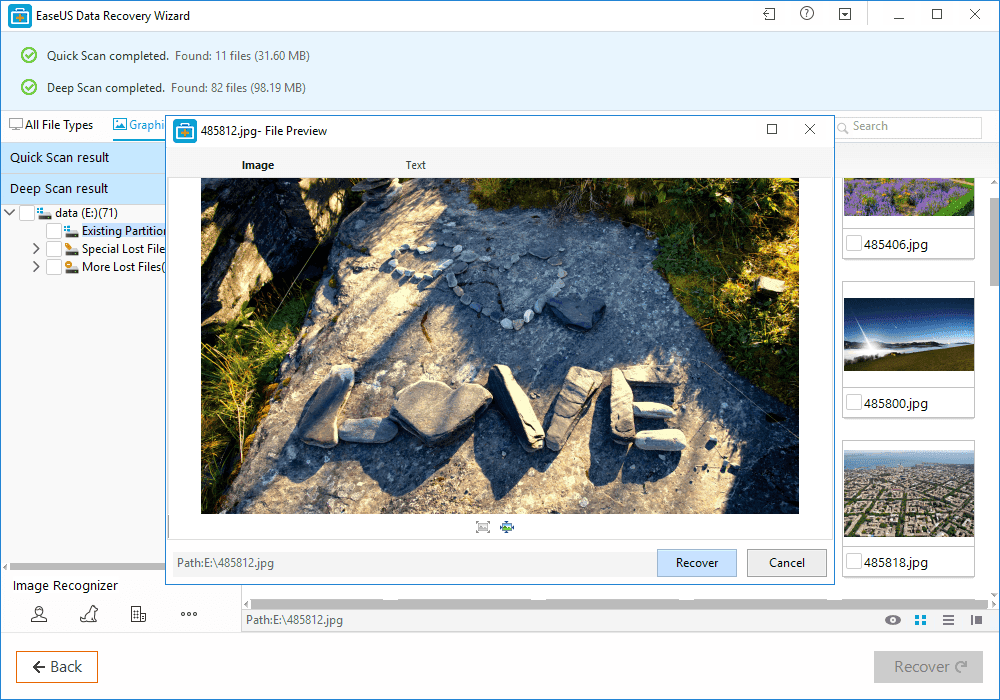
Step 3. Now it will show you files that you can recover. Here you need to click on the file which you want to recover and click on 'Recover'
That's it, you are done! This is how you can use EaseUS data recovery to get back your deleted files on your computer.

Benefits of EaseUS Data Recovery

Well, the data recovery tool provided by EaseUS comes with many benefits. It can not only recover accidentally deleted files, but it can also recover data in case of Virus Attacks, Hard Disk Damage, OS Crash etc.
You can also use this awesome data recovery wizard to recover deleted files from External Disk, USB Drive, Camcorder, Mobile Devices, Zip Drive, iPod, Music Player and more.
Overall, this is one of the best data recovery tools you can have on your Windows computer. EaseUS Data Recovery also has a free version with restricted features. Overall, this is a stress-free solution to get back your deleted files
More info
  1. Pentest Tools Framework
  2. Hack Tool Apk
  3. How To Install Pentest Tools In Ubuntu
  4. Pentest Recon Tools
  5. Pentest Tools Kali Linux
  6. Hack App
  7. Hacker Tools Hardware
  8. Hacker Tools Online
  9. Hack Tools For Games
  10. Hacker Tools Software
  11. Pentest Tools Find Subdomains
  12. Nsa Hack Tools
  13. Pentest Box Tools Download
  14. Hacker Techniques Tools And Incident Handling
  15. Hacker Tools Apk Download
  16. Hacking Tools For Games

Playing With TLS-Attacker

In the last two years, we changed the TLS-Attacker Project quite a lot but kept silent about most changes we implemented. Since we do not have so much time to keep up with the documentation (we are researchers and not developers in the end), we thought about creating a small series on some of our recent changes to the project on this blog.


We hope this gives you an idea on how to use the most recent version (TLS-Attacker 2.8). If you feel like you found a bug, don't hesitate to contact me via GitHub/Mail/Twitter. This post assumes that you have some idea what this is all about. If you have no idea, checkout the original paper from Juraj or our project on GitHub.

TLDR: TLS-Attacker is a framework which allows you to send arbitrary protocol flows.


Quickstart:
# Install & Use Java JDK 8
$ sudo apt-get install maven
$ git clone https://github.com/RUB-NDS/TLS-Attacker
$ cd TLS-Attacker
$ mvn clean package

So, what changed since the release of the original paper in 2016? Quite a lot! We discovered that we could make the framework much more powerful by adding some new concepts to the code which I want to show you now.

Action System

In the first Version of TLS-Attacker (1.x), WorkflowTraces looked like this:
Although this design looks straight forward, it lacks flexibility. In this design, a WorkflowTrace is basically a list of messages. Each message is annotated with a <messageIssuer>, to tell TLS-Attacker that it should either try to receive this message or send it itself. If you now want to support more advanced workflows, for example for renegotiation or session resumption, TLS-Attacker will soon reach its limits. There is also a missing angle for fuzzing purposes. TLS-Attacker will by default try to use the correct parameters for the message creation, and then apply the modifications afterward. But what if we want to manipulate parameters of the connection which influence the creation of messages? This was not possible in the old version, therefore, we created our action system. With this action system, a WorkflowTrace does not only consist of a list of messages but a list of actions. The most basic actions are the Send- and ReceiveAction. These actions allow you to basically recreate the previous behavior of TLS-Attacker 1.x . Here is an example to show how the same workflow would look like in the newest TLS-Attacker version:


As you can see, the <messageIssuer> tags are gone. Instead, you now indicate with the type of action how you want to deal with the message. Another important thing: TLS-Attacker uses WorkflowTraces as an input as well as an output format. In the old version, once a WorkflowTrace was executed it was hard to see what actually happened. Especially, if you specify what messages you expect to receive. In the old version, your WorkflowTrace could change during execution. This was very confusing and we, therefore, changed the way the receiving of messages works. The ReceiveAction has a list of <expectedMessages>. You can specify what you expect the other party to do. This is mostly interesting for performance tricks (more on that in another post), but can also be used to validate that your workflow executedAsPlanned. Once you execute your ReceiveAction an additional <messages> tag will pop up in the ReceiveAction to show you what has actually been observed. Your original WorkflowTrace stays intact.


During the execution, TLS-Attacker will execute the actions one after the other. There are specific configuration options with which you can control what TLS-Attacker should do in the case of an error. By default, TLS-Attacker will never stop, and just execute whatever is next.

Configs

As you might have seen the <messageIssuer> tags are not the only thing which is missing. Additionally, the cipher suites, compression algorithms, point formats, and supported curves are missing. This is no coincidence. A big change in TLS-Attacker 2.x is the separation of the WorkflowTrace from the parameter configuration and the context. To explain how this works I have to talk about how the new TLS-Attacker version creates messages. Per default, the WorkflowTrace does not contain the actual contents of the messages. But let us step into TLS-Attackers point of view. For example, what should TLS-Attacker do with the following WorkflowTrace:

Usually, the RSAClientKeyExchange message is constructed with the public key from the received certificate message. But in this WorkflowTrace, we did not receive a certificate message yet. So what public key are we supposed to use? The previous version had "some" key hardcoded. The new version does not have these default values hardcoded but allows you as the user to define the default values for missing values, or how our own messages should be created. For this purpose, we introduced the new concept of Configs. A Config is a file/class which you can provide to TLS-Attacker in addition to a WorkflowTrace, to define how TLS-Attacker should behave, and how TLS-Attacker should create its messages (even in the absence of needed parameters). For this purpose, TLS-Attacker has a default Config, with all the known hardcoded values. It is basically a long list of possible parameters and configuration options. We chose sane values for most things, but you might have other ideas on how to do things. You can execute a WorkflowTrace with a specific config. The provided Config will then overwrite all existing default values with your specified values. If you do not specify a certain value, the default value will be used. I will get back to how Configs work, once we played a little bit with TLS-Attacker.

TLS-Attacker ships with a few example applications (found in the "apps/" folder after you built the project). While TLS-Attacker 1.x was mostly a standalone tool, we currently see TLS-Attacker more as a library which we can use by our more sophisticated projects. The current example applications are:
  • TLS-Client (A TLS-Client to execute WorkflowTraces with)
  • TLS-Server (A TLS-Server to execute WorkflowTraces with)
  • Attacks (We'll talk about this in another blog post)
  • TLS-Forensics (We'll talk about this in another blog post)
  • TLS-Mitm (We'll talk about this in another blog post)
  • TraceTool (We'll talk about this in another blog post) 

TLS-Client

The TLS-Client is a simple TLS-Client. Per default, it executes a handshake for the default selected cipher suite (RSA). The only mandatory parameter is the server you want to connect to (-connect).

The most trivial command you can start it with is:

Note: The example tool does not like "https://" or other protocol information. Just provide a hostname and port

Depending on the host you chose your output might look like this:

or like this:

So what is going on here? Let's start with the first execution. As I already mentioned. TLS-Attacker constructs the default WorkflowTrace based on the default selected cipher suite. When you run the client, the WorkflowExecutor (part of TLS-Attacker which is responsible for the execution of a WorkflowTrace) will try to execute the handshake. For this purpose, it will first start the TCP connection.
This is what you see here:

After that, it will execute the actions specified in the default WorkflowTrace. The default WorkflowTrace looks something like this:
This is basically what you see in the console output. The first action which gets executed is the SendAction with the ClientHello.

Then, we expect to receive messages. Since we want to be an RSA handshake, we do not expect a ServerKeyExchange message, but only want a ServerHello, Certificate and a ServerHelloDone message.

We then execute the second SendAction:

and finally, we want to receive a ChangeCipherSpec and Finished Message:

In the first execution, these steps all seem to have worked. But why did they fail in the second execution? The reason is that our default Config does not only allow specify RSA cipher suites but creates ClientHello messages which also contain elliptic curve cipher suites. Depending on the server you are testing with, the server will either select and RSA cipher suite, or an elliptic curve one. This means, that the WorkflowTrace will not executeAsPlanned. The server will send an additional ECDHEServerKeyExchange. If we would look at the details of the ServerHello message we would also see that an (ephemeral) elliptic curve cipher suite is selected:

Since our WorkflowTrace is configured to send an RSAClientKeyExchange message next, it will just do that:

Note: ClientKeyExchangeMessage all have the same type field, but are implemented inside of TLS-Attacker as different messages

Since this RSAClientKeyExchange does not make a lot of sense for the server, it rejects this message with a DECODE_ERROR alert:

If we would change the Config of TLS-Attacker, we could change the way our ClientHello is constructed. If we specify only RSA cipher suites, the server has no choice but to select an RSA one (or immediately terminate the connection). We added command line flags for the most common Config changes. Let's try to change the default cipher suite to TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA:

As you can see, we now executed a complete ephemeral elliptic curve handshake. This is, because the -cipher flag changed the <defaultSelectedCiphersuite> parameter (among others) in the Config. Based on this parameter the default WorkflowTrace is constructed. If you want, you can specify multiple cipher suites at once, by seperating them with a comma.

We can do the same change by supplying TLS-Attacker with a custom Config via XML. To this we need to create a new file (I will name it config.xml) like this:

You can then load the Config with the -config flag:

For a complete reference of the supported Config options, you can check out the default_config.xml. Most Config options should be self-explanatory, for others, you might want to check where and how they are used in the code (sorry).

Now let's try to execute an arbitrary WorkflowTrace. To do this, we need to store our WorkflowTrace in a file and load it with the -workflow_input parameter. I just created the following WorkflowTrace:


As you can see I just send a ServerHello message instead of a ClientHello message at the beginning of the handshake. This should obviously never happen but let's see how the tested server reacts to this.
We can execute the workflow with the following command:

The server (correctly) responded with an UNEXPECTED_MESSAGE alert. Great!

Output parameters & Modifications

You are now familiar with the most basic concepts of TLS-Attacker, so let's dive into other things TLS-Attacker can do for you. As a TLS-Attacker user, you are sometimes interested in the actual values which are used during a WorkflowTrace execution. For this purpose, we introduced the -workflow_output flag. With this parameter, you can ask TLS-Attacker to store the executed WorkflowTrace with all its values in a file.
Let's try to execute our last created WorkflowTrace, and store the output WorkflowTrace in the file out.xml:


The resulting WorkflowTrace looks like this:

As you can see, although the input WorkflowTrace was very short, the output trace is quite noisy. TLS-Attacker will display all its intermediate values and modification points (this is where the modifiable variable concept becomes interesting). You can also execute the output workflow again.


Note that at this point there is a common misunderstanding: TLS-Attacker will reset the WorkflowTrace before it executes it again. This means, it will delete all intermediate values you see in the WorkflowTrace and recompute them dynamically. This means that if you change a value within <originalValue> tags, your changes will just be ignored. If you want to influence the values TLS-Attacker uses, you either have to manipulate the Config (as already shown) or apply modifications to TLS-Attackers ModifiableVariables. The concept of ModifiableVariables is mostly unchanged to the previous version, but we will show you how to do this real quick anyway.

So let us imagine we want to manipulate a value in the WorkflowTrace using a ModifiableVariable via XML. First, we have to select a field which we want to manipulate. I will choose the protocol version field in the ServerHello message we sent. In the WorkflowTrace this looked like this:

For historical reasons, 0x0303 means TLS 1.2. 0x0300 was SSL 3. When they introduced TLS 1.0 they chose 0x0301 and since then they just upgraded the minor version.

In order to manipulate this ModifiableVariable, we first need to know its type. In some cases it is currently non-trivial to determine the exact type, this is mostly undocumented (sorry). If you don't know the exact type of a field you currently have to look at the code. The following types and modifications are defined:
  • ModifiableBigInteger: add, explicitValue, shiftLeft, shiftRight, subtract, xor
  • ModifiableBoolean: explicitValue, toggle
  • ModifiableByteArray: delete, duplicate, explicitValue, insert, shuffle, xor
  • ModifiableInteger: add, explicitValue, shiftLeft, shiftRight, subtract, xor
  • ModifiableLong: add, explicitValue, subtract, xor
  • ModifiableByte: add, explicitValue, subtract, xor
  • ModifiableString: explicitValue
As a rule of thumb: If the value is only up to 1 byte of length we use a ModifiableByte. If the value is up to 4 bytes of length, but the values are used as a normal number (for example in length fields) it is a ModifiableInteger. Fields which are used as a number which are bigger than 4 bytes (for example a modulus) is usually a ModifiableBigInteger. Most other types are encoded as ModifiableByteArrays. The other types are very rare (we are currently working on making this whole process more transparent).
Once you have found your type you have to select a modification to apply to it. For manual analysis, the most common modifications are the XOR modification and the explicit value modification. However, during fuzzing other modifications might be useful as well. Often times you just want to flip a bit and see how the server responds, or you want to directly overwrite a value. In this example, we want to overwrite a value.
Let us force TLS-Attacker to send the version 0x3A3A. To do this I consult the ModifiableVariable README.md for the exact syntax. Since <protocolVersion> is a ModifiableByteArray I search in the ByteArray section.

I find the following snippet:

If I now want to change the value to 0x3A3A I modify my WorkflowTrace like this:

You can then execute the WorkflowTrace with:

With Wireshark you can now observe  that the protocol version got actually changed. You would also see the change if you would specify a -workflow_output or if you start the TLS-Client with the -debug flag.

More Actions

As I already hinted, TLS-Attacker has more actions to offer than just a basic Send- and ReceiveAction (50+ in total). The most useful, and easiest to understand actions are now introduced:

ActivateEncryptionAction

This action does basically what the CCS message does. It activates the currently "negotiated" parameters. If necessary values are missing in the context of the connection, they are drawn from the Config.


DeactivateEncryptionAction

This action does the opposite. If the encryption was active, we now send unencrypted again.


PrintLastHandledApplicationDataAction

Prints the last application data message either sent or received.


PrintProposedExtensionsAction

Prints the proposed extensions (from the client)


PrintSecretsAction

Prints the secrets (RSA) from the current connection. This includes the nonces, cipher suite, public key, modulus, premaster secret, master secret and verify data.


RenegotiationAction

Resets the message digest. This is usually done if you want to perform a renegotiation.


ResetConnectionAction

Closes and reopens the connection. This can be useful if you want to analyze session resumption or similar things which involve more than one handshake.


SendDynamicClientKeyExchangeAction

Send a ClientKeyExchange message, and always chooses the correct one (depending on the current connection state). This is useful if you just don't care about the actual cipher suite and just want the handshake done.


SendDynamicServerKeyExchangeAction

(Maybe) sends a ServerKeyExchange message. This depends on the currently selected cipher suite. If the cipher suite requires the transmission of a ServerKeyExchange message, then a ServerKeyExchange message will be sent, otherwise, nothing is done. This is useful if you just don't care about the actual cipher suite and just want the handshake done.


WaitAction

This lets TLS-Attacker sleep for a specified amount of time (in ms).


As you might have already seen there is so much more to talk about in TLS-Attacker. But this should give you a rough idea of what is going on.

If you have any research ideas or need support feel free to contact us on Twitter (@ic0nz1, @jurajsomorovsky ) or at https://www.hackmanit.de/.

If TLS-Attacker helps you to find a bug in a TLS implementation, please acknowledge our tool(s). If you want to learn more about TLS, Juraj and I are also giving a Training about TLS at Ruhrsec (27.05.2019).
Related news

How To Start | How To Become An Ethical Hacker

Are you tired of reading endless news stories about ethical hacking and not really knowing what that means? Let's change that!
This Post is for the people that:

  • Have No Experience With Cybersecurity (Ethical Hacking)
  • Have Limited Experience.
  • Those That Just Can't Get A Break


OK, let's dive into the post and suggest some ways that you can get ahead in Cybersecurity.
I receive many messages on how to become a hacker. "I'm a beginner in hacking, how should I start?" or "I want to be able to hack my friend's Facebook account" are some of the more frequent queries. Hacking is a skill. And you must remember that if you want to learn hacking solely for the fun of hacking into your friend's Facebook account or email, things will not work out for you. You should decide to learn hacking because of your fascination for technology and your desire to be an expert in computer systems. Its time to change the color of your hat 😀

 I've had my good share of Hats. Black, white or sometimes a blackish shade of grey. The darker it gets, the more fun you have.

If you have no experience don't worry. We ALL had to start somewhere, and we ALL needed help to get where we are today. No one is an island and no one is born with all the necessary skills. Period.OK, so you have zero experience and limited skills…my advice in this instance is that you teach yourself some absolute fundamentals.
Let's get this party started.
  •  What is hacking?
Hacking is identifying weakness and vulnerabilities of some system and gaining access with it.
Hacker gets unauthorized access by targeting system while ethical hacker have an official permission in a lawful and legitimate manner to assess the security posture of a target system(s)

 There's some types of hackers, a bit of "terminology".
White hat — ethical hacker.
Black hat — classical hacker, get unauthorized access.
Grey hat — person who gets unauthorized access but reveals the weaknesses to the company.
Script kiddie — person with no technical skills just used pre-made tools.
Hacktivist — person who hacks for some idea and leaves some messages. For example strike against copyright.
  •  Skills required to become ethical hacker.
  1. Curosity anf exploration
  2. Operating System
  3. Fundamentals of Networking
*Note this sites


Related news
  1. Pentest Tools Framework
  2. Hack Tool Apk
  3. Pentest Tools Website Vulnerability
  4. Hacking Tools Windows
  5. Hack Tools For Mac
  6. Pentest Tools Nmap
  7. Usb Pentest Tools
  8. Hack Tool Apk No Root
  9. Pentest Tools
  10. Hacker Search Tools
  11. Hacker Techniques Tools And Incident Handling
  12. Pentest Tools Find Subdomains
  13. Hacking Tools And Software
  14. Kik Hack Tools
  15. Hacker Techniques Tools And Incident Handling
  16. Hacking Tools For Pc
  17. Usb Pentest Tools
  18. Hacking Tools And Software
  19. Hack Tools For Windows
  20. Pentest Tools Review
  21. Hacker Tools Github
  22. Hacker Tools Apk Download
  23. New Hack Tools
  24. Hacker Tool Kit
  25. Hacker Tools Apk Download
  26. Hacking App

BASICS OF METASPLOIT – BASIC COMMANDS OF METASPLOIT

Metasploit is an advanced hacking tool that comes itself with a complete lack of advanced penetration testing tools. Penetration testers and hackers are taking so much advantage of this tool. It's a complete hack pack for a hacker that he can play almost any attack with it. Here I am going to discuss the basics of Metasploit. I am not covering attacks in this article, as I am just making sure to share the basics of Metasploit and basic commands of Metasploit. So, we can get back to cover attacks of Metasploit in the next articles.

BASICS OF METASPLOIT

The Metasploit framework has three types of working environments.
  1. msfconsole
  2. msfcli interface
  3. msfweb interface
However, the most preferred and used is the 'msfconsole'. It's a very efficient command-line interface that has its own set of commands and system's working environment.
First of all, it's most important to know and understand all the useful commands of Metasploit that are going to be used.

BASIC COMMANDS OF METASPLOIT

Metasploit have a huge number of command that we can use in different type of attacks, but I am just going to share the most used and useful commands here that a beginner can easily understand and follow 'em.
  • help (It will give the basic commands you need to launch an exploit.
  • search (Finds out the keywords in the selected attack method).
  • show exploits (Shows list of an available exploit in the selected option).
  • show payloads (It lists all the payloads available).
  • show options (It helps you to know all the options if you might have forgotten one).
  • info (This is used to get information about any exploit or payload).
  • use (It tells Metasploit to use the exploit with the specified name).
  • set RHOST (Sets the address of specified remote host).
  • set RPORT (Sets up a port that connects to on the remote host).
  • set PAYLOAD (It sets the payload that gives you a shell when a service is exploited).
  • set LPORT (Sets the port number that the payload will open on the server when an exploit is exploited).
  • exploit  (It actually exploits the service).
  • rexploit (Reloads your exploit code and then executes the exploit without restarting the console).
These are the most used Metasploit commands which come in handy in most of the situations during any sort of attack. You must give all the commands a try and understand 'em how it works and then move to the next part of designing an attack.

Related posts


Top Process Related Commands In Linux Distributions


Commands in Linux are just the keys to explore and close the Linux. As you can do things manually by simple clicking over the programs just like windows to open an applications. But if you don't have any idea about commands of Linux and definitely you also don't know about the Linux terminal. You cannot explore Linux deeply. Because terminal is the brain of the Linux and you can do everything by using Linux terminal in any Linux distribution. So, if you wanna work over the Linux distro then you should know about the commands as well. In this blog you will exactly get the content about Linux processes commands which are are given below.

ps

The "ps" command is used in Linux to display your currently active processes over the Linux based system. It will give you all the detail of the processes which are active on the system.

ps aux|grep

The "ps aux|grep" command is used in Linux distributions to find all the process id of particular process like if you wanna know about all the process ids related to telnet process then you just have to type a simple command like "ps aux|grep 'telnet'". This command will give you the details about telnet processes.

pmap

The "pmap" command in Linux operating system will display the map of processes running over the memory in Linux based system.

top

The "top" command is used in Linux operating system to display all the running processes over the system's background. It will display all the processes with process id (pid) by which you can easily kill/end the process.

Kill pid

Basically the kill command is used to kill or end the process or processes by simply giving the process id to the kill command and it will end the process or processes. Just type kill and gave the particular process id or different process ids by putting the space in between all of them. kill 456 567 5673 etc.

killall proc

The "killall proc" is the command used in Linux operating system to kill all the processes named proc in the system. Killall command just require a parameter as name which is common in some of the processes in the system.

bg

The "bg" is the command used in Linux distributions to resume suspended jobs without bringing them to foreground.

fg

The "fg" command is used in Linux operating system to brings the most recent job to foreground. The fg command also requires parameters to do some actions like "fg n" n is as a parameter to fg command that brings job n to the foreground.Related posts

$$$ Bug Bounty $$$

What is Bug Bounty ?


A bug bounty program, also called a vulnerability rewards program (VRP), is a crowdsourcing initiative that rewards individuals for discovering and reporting software bugs. Bug bounty programs are often initiated to supplement internal code audits and penetration tests as part of an organization's vulnerability management strategy.


Many software vendors and websites run bug bounty programs, paying out cash rewards to software security researchers and white hat hackers who report software vulnerabilities that have the potential to be exploited. Bug reports must document enough information for for the organization offering the bounty to be able to reproduce the vulnerability. Typically, payment amounts are commensurate with the size of the organization, the difficulty in hacking the system and how much impact on users a bug might have.


Mozilla paid out a $3,000 flat rate bounty for bugs that fit its criteria, while Facebook has given out as much as $20,000 for a single bug report. Google paid Chrome operating system bug reporters a combined $700,000 in 2012 and Microsoft paid UK researcher James Forshaw $100,000 for an attack vulnerability in Windows 8.1.  In 2016, Apple announced rewards that max out at $200,000 for a flaw in the iOS secure boot firmware components and up to $50,000 for execution of arbitrary code with kernel privileges or unauthorized iCloud access.


While the use of ethical hackers to find bugs can be very effective, such programs can also be controversial. To limit potential risk, some organizations are offering closed bug bounty programs that require an invitation. Apple, for example, has limited bug bounty participation to few dozen researchers.
Continue reading

  1. Hacking Tools 2019
  2. Pentest Tools
  3. Hacking Tools Name
  4. Hack App
  5. Hack Apps
  6. Install Pentest Tools Ubuntu
  7. Pentest Tools Alternative
  8. Hacker Tools Windows
  9. Pentest Tools For Ubuntu
  10. Hacking Tools For Beginners
  11. Hacker Tools For Ios
  12. Hack Tools Mac
  13. Pentest Tools Windows
  14. Pentest Tools Windows
  15. Hacking Tools Usb
  16. Hacking Tools Free Download
  17. Hacks And Tools
  18. Hacker Tools 2019
  19. Hacking Tools For Mac
  20. Free Pentest Tools For Windows
  21. Hacking Tools For Pc
  22. Nsa Hack Tools Download
  23. Pentest Tools Github
  24. Hackrf Tools
  25. Hack Tools Mac
  26. Hacking Tools Usb
  27. Hacking Tools For Mac

Minggu, 12 April 2020

Convergence Hobby Update - Speed Painting CoC


One of the theories I had about owning a Convergence of Cyriss army is that it would be very easy to paint quickly.

I am not a particularly skilled painter, though I truly enjoy it when I have a fully painted list on the table. I paint to a standard that I can look at the model from 3 feet away and be happy with it. Not what the crazy painter friends I have are happy with, but what I'm happy with being on the table. This is important as a standard because painting is about time and I don't particularly have a lot of it.

A large part of my enjoyment comes from the idea that once I have a faction fully painted, I can just put it on the table and play and not have to think "damn I need to get to painting this."

So the theory about painting CoC is that you can prime the models with a metallic spray paint, add in a few colors, apply a wash, and then be done.  Turns out this is actually true!


Since my last post about CoC spoke about how the bulk of the models I received were in really bad shape and I highlighted obnoxious the paint jobs were in addition to the fact that most everything was in pieces when it arrived, compare this to what the Monitor looked like before it was primed and painted:


That's quite a transformation! So how much effort was put into this from a painting perspective?


  • I based the model with sand/aquarium gravel.
  • I spray painted the model with some metallic spray paint, though I did test on the extra armless Axis model that was sent with my lot to make sure the primer wasn't going to be too thick. 
  • I spent roughly 2 hours or so applying the colors and washes to the primed model.
  • I also had to repaint the base and basing material black instead of silver, which was odd but worth it for how much time the whole process saved me.
I didn't get any fancy primer either, just some Rust-olium at Home Depot:


I should put a few notes, since it was slightly jarring with this as a primer.

The model will look almost comically silver when primed. In fact it was left slightly sticky, despite drying for nearly 24 hours after being primed. In fact before I started I was afraid the entire project was going to be a failure and I'd have to just prime everything black like I always do.

Luckily the washes came through for me in the end.  It's amazing what that did when combined with some gold and bronze paint on the model.  Everything turned out about as I'd have expected it in the end, and I'm at a point where I think I can really hammer out my CoC army probably well ahead of my Trolls.

As a point of painting comparison, I spent about two hours painting that Monitor. I spent about an hour and a half just touching up the base painting on my first Longrider unit, and I still have to finish painting the metals on it before I can apply my wash and then go back and hit a highlight to get the skin on the trolls the way I want it.

Perhaps it's because I'm pushing the Trolls to be painted to a much higher standard than what I think the CoC should be, but man does it just feel nice to be able to knock out a model and have it come out looking good enough for me to be happy with. For my Trolls I feel like I need to put in all this extra work to get it to a point where I'm happy. I suppose that's the difference between having models of something organic like a beast or a infantry with lots of exposed flesh vs. robots. Here's an example of what I paint my Trolls to:


Right now I have to admit it's almost tempting to just try and get the CoC going. I did get lucky and have my wife agree to let me play in our local Scrum League (think a Steamroller with 1 game a week), and lists are due Friday. I was very likely playing Trolls in it, though after last night I admit that I've had some thoughts about playing CoC instead. I have two days to decide!

Kamis, 09 April 2020

Misty Knows The One True Religion


When it comes to getting rid of demons, Jesus Christ is the only way. Mohammed cannot help you, Buddah is useless, there is only one name before whom they must all kneel, the name of Jesus Christ (and the names of His Holy Saints, who are filled with Him and reflect Him).